Project 2026 · Python · FastAPI · LLM · GDPR

Internal AI Ops Assistant

An internal AI service for a healthcare company: it answers policy questions with sources, turns incoming documents into validated data and triages tickets from Jira to Microsoft Teams. Personal data is removed before any model call, and a human reviews everything sensitive.

Photo of Amrina
Amrina

Three everyday problems

Each one runs as an API, in the web interface and through integrations.

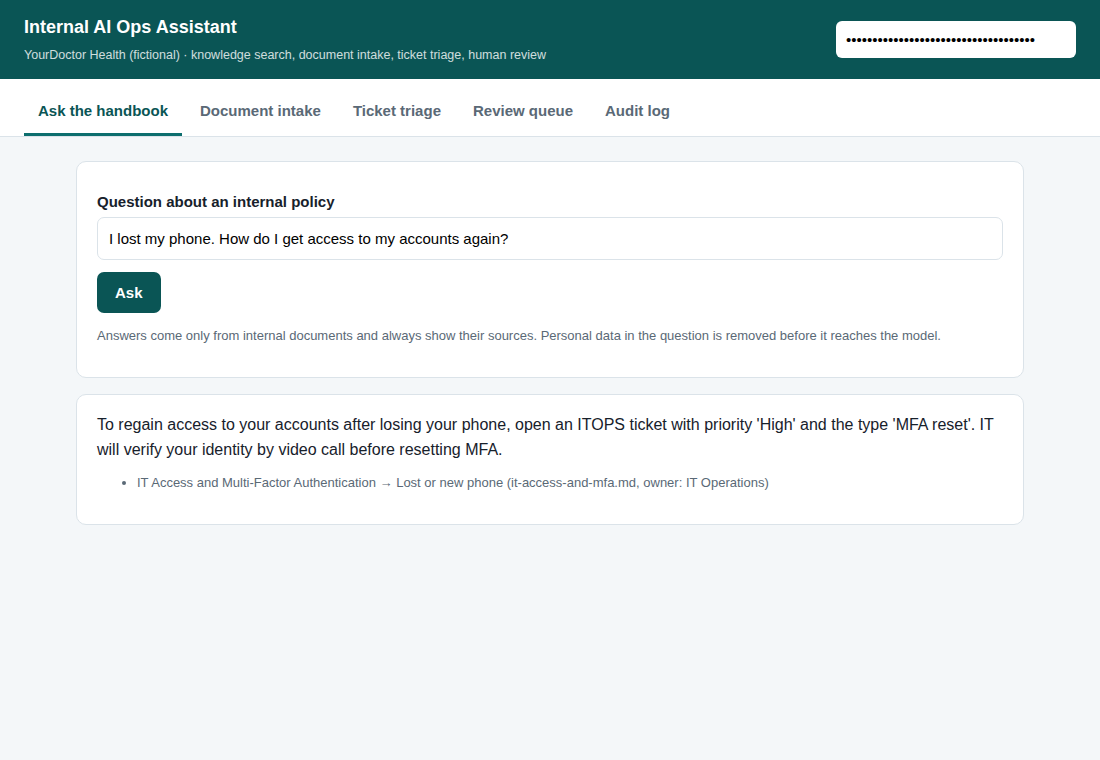
Knowledge search

Answers questions about internal policies with the exact source, or says honestly that the documents do not cover it.

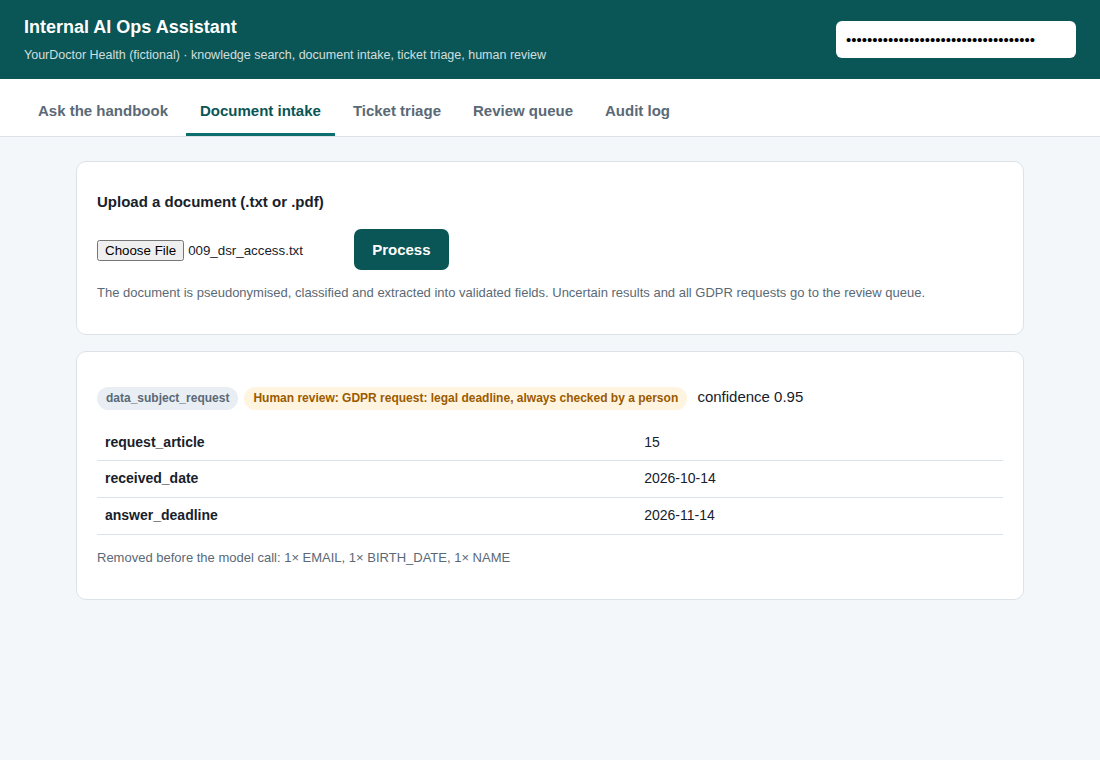
Document intake

Classifies emails, invoices, doctor applications and GDPR requests and extracts validated fields. Legal deadlines are computed in code.

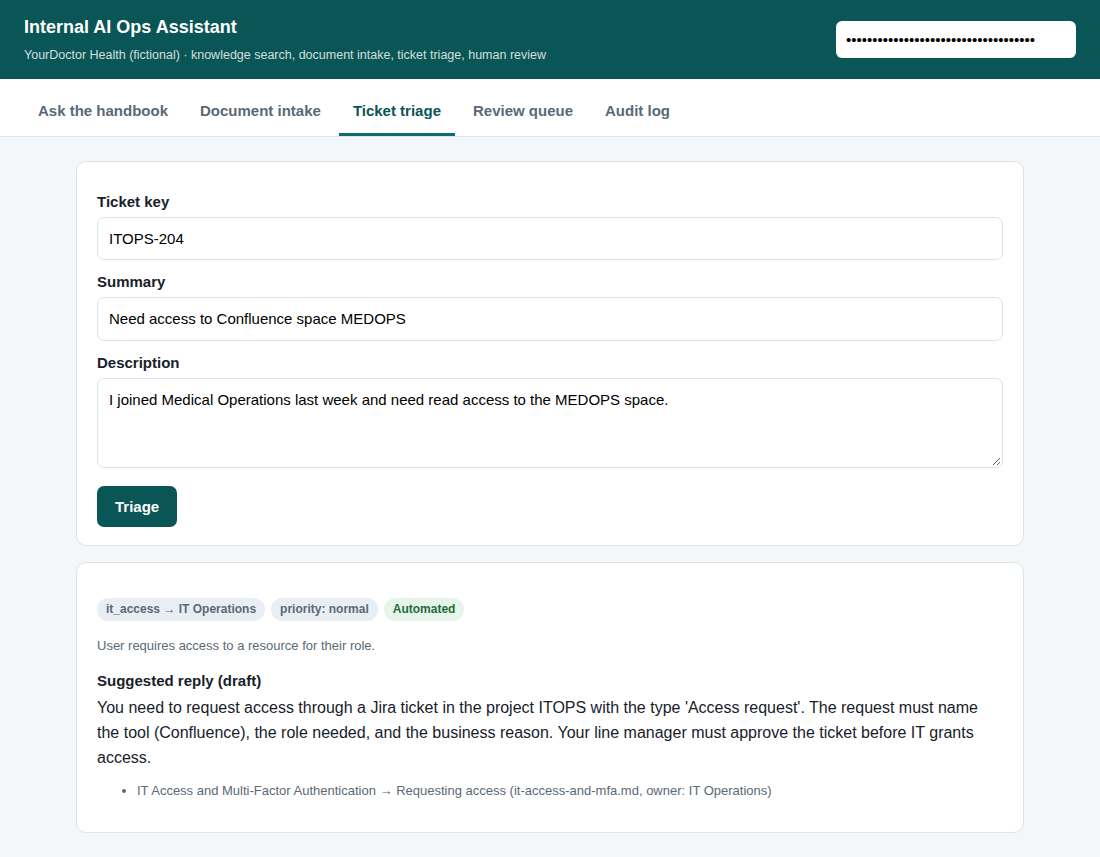
Ticket triage

Jira webhook in, category, priority, team and a cited reply draft out, posted to Microsoft Teams. Sensitive tickets go to a person.

Measured, not assumed

gpt-4o-mini on small, self-made labelled sets (see the README for the caveats and the first-run results).

100%of answerable questions answered with the correct source; 2 of 2 off-topic questions refused
44 / 44document fields extracted correctly across 12 documents
8 / 8tickets with correct category and priority; all sensitive ones sent to a human

In the interface

Answer with its source document
Knowledge search: a short answer with the policy section it comes from.
GDPR request extracted and sent to review
A GDPR access request: fields extracted, deadline computed, personal data removed, sent to review.
Ticket triaged to IT Operations with reply draft
A routine ticket: routed to IT Operations with a cited reply draft.

Built for a regulated environment

ConcernWhat the service does
Patient dataPseudonymises emails, phone numbers, IBANs, insurance numbers, birth dates and names before any model call; logs never contain document text; can run on a self-hosted model (Ollama)
Human oversightReview queue for low confidence, failed validation, GDPR requests and security tickets; approve, correct or reject; full audit trail
Access and secretsRole-based API keys stored as hashes, HMAC-signed webhooks with deduplication, secrets only from the environment
IntegrationsJira, Microsoft Teams, Confluence, SharePoint (Graph), Nextcloud (WebDAV), plus an n8n low-code workflow
OperationsJSON logs with request IDs, Prometheus metrics, health and readiness checks, Docker, CI with lint, security rules, 23 tests and a Docker build

Connectors are tested against mocked API responses, not against a live company tenant. YourDoctor Health and all data in the project are fictional.